Category: Threat Hunting

Detect and Investigate DNS Tunneling
SIEM
Prajwal V

DNS Tunneling: #1 Threat Hunting Guide to Master

Introduction DNS tunneling is one of the most elusive and dangerous tactics cybercriminals use to bypass security protocols. By exploiting the Domain Name System (DNS), attackers create hidden channels of communication, allowing them to exfiltrate data or communicate with malicious servers unnoticed. For organizations, DNS tunneling presents a major challenge because traditional security tools like firewalls and intrusion detection systems (IDS) often miss this type of attack. In this comprehensive

Read More »
SIEM Use Cases
SIEM
Prajwal V

6 Real-World SIEM Use Cases: Increase Your SOC’s Potential

Real-World SIEM Applications: Harness the Potential of Your Security Operations Center Are you seeking to strengthen the security of your organization? Discovering real-world SIEM use cases will allow you to unleash your cloud security to its full potential, using SIEM technology to detect advanced threats, protect against data breaches, and more. In this blog post, we will highlight six SIEM use cases that can significantly boost the capabilities of your

Read More »
sysmon event ids
SOC
Prajwal V

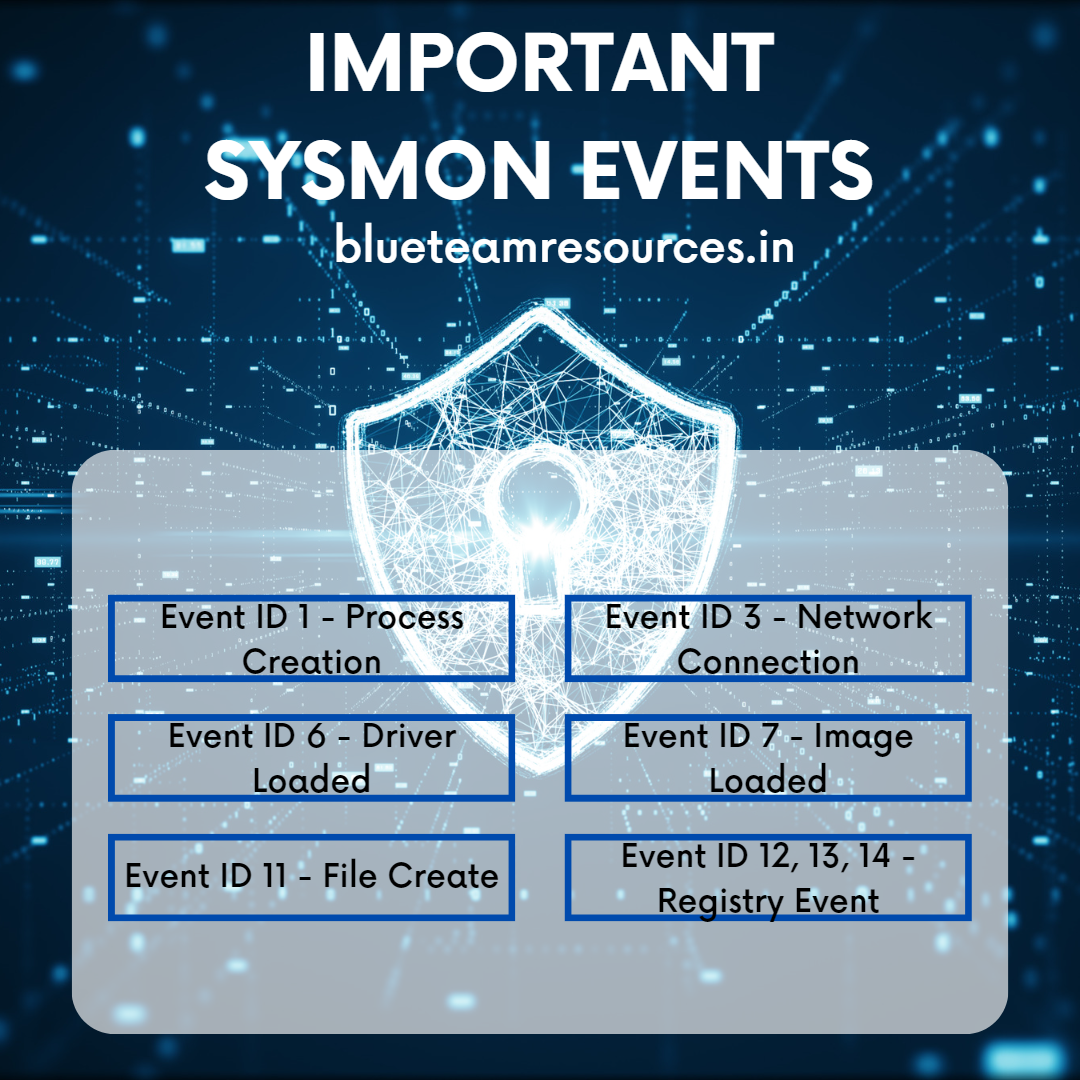
Enhance Security Monitoring by Mastering Sysmon Event IDs

Understanding Sysmon Event IDs for Improved Security Monitoring Effective security monitoring is vital to creating and maintaining a safe IT environment. Sysmon Event IDs offer invaluable insight into any potentially malicious activity on your network; in this post we explore this subject further and suggest using them for enhanced monitoring purposes. What is Sysmon (System Monitor)? Sysmon is a Windows service and device driver which remains active after system reboots

Read More »
event id 4624 and 4625
SIEM
Prajwal V

Splunking Event ID 4624 and 4625: Best Security Guide

Splunk Correlation Rules for Windows Event ID 4624 and 4625 Monitoring and analyzing Windows Event Logs is a critical element of any organization’s security strategy. Of the many events recorded, Windows Event ID 4624 (successful first logon session) and 4625 (failed new logon session) can be particularly helpful for detecting potential security threats. In this blog post, we’ll walk you through creating a Splunk correlation rule that utilizes these two

Read More »
Threat Hunting Guide
Threat Hunting
Prajwal V

#1 Ultimate Threat Hunting Guide – Get Started

Introduction: Exploring the Maze of Cyber Threat Hunting – A Deep Dive into Techniques and Tools In the intricate landscape of digital security, where malicious activities and cyber threats lurk behind every corner, cyber threat hunting emerges as a robust approach to threat management. Unlike the standard process of security detection technology, which relies on blocking known threats, threat hunting embodies a proactive approach. It’s akin to delving into a

Read More »

Subscribe To Our Newsletter